One system of record for every IT policy, control, and review cycle.
As cybersecurity risks evolve and grow more complex, keeping IT operations aligned with regulatory requirements and business objectives gets harder every year. Sigmify GRC gives teams one place to define policies, enforce controls, and collect evidence, instead of juggling separate tools on separate timelines.
Unified Control Library
A single source of truth for IT controls, policies, and compliance requirements, mapped across frameworks including ISO, SOC, Central Bank, and NIST.
SIEM + HRM Integrated Monitoring
Real time monitoring and event correlation give you continuous compliance visibility, so the control lifecycle stops eating up manual hours.
Policy & Workflow Automation
Purpose built policy management and workflow automation keep every control, policy, and review cycle in one place, not scattered across tools.
Eight systems most teams run separately. Sigmify GRC runs them as one.
Each capability below maps directly to a stage of the governance lifecycle, from defining a control, to enforcing it, to proving it held up under audit.
Unified Control Library & Policy Mapping
- One control library holds every IT control, policy, and compliance requirement, so nobody’s hunting across spreadsheets and shared drives.
- Everything is mapped to the frameworks you already answer to, including ISO, SOC, Central Bank, and NIST.
- SIEM and HRM data feed the library continuously, so gaps get caught early instead of at the next manual review.
Governance Policy Framework
Administrators publish and enforce IT policies with clear ownership, version control, and review cycles, and every change is backed by audit trails and monitoring insights pulled straight from SIEM and HRM activity.
Workflow Synchronization & Reviewer Assignment
- Governance tasks like access reviews, configuration checks, and patch validations run on their own, not on someone’s to-do list.
- SIEM and HRM alerts and system events are what actually trigger the work.
- Reviewers get notified, escalation paths are already defined, and status updates in real time.
Evidence & Document Repository
Logs, approvals, and supporting artifacts land in one secure, permission controlled repository, with SIEM and HRM integrated collection quietly capturing and consolidating everything so records stay audit ready without anyone chasing paperwork.
Compliance Tracking & Deviations
- Dashboards correlate SIEM and HRM alerts with control status for real time visibility into where things stand.
- Overdue tasks and deviations get flagged as they happen, not weeks later.
- Ongoing correlation makes it easier to remediate before an issue becomes a finding.
Audit Readiness & Management
- Compliance activities, evidence, and approvals are already organized into structured, audit ready trails.
- SIEM and HRM logs plus automated workflows make audit preparation and auditor collaboration far less painful.
- See our Global Security & Compliance Standards hub for the full audit readiness workflow.
Exception & Escalation Management
The platform tracks task completion, flags failed controls, and triggers automated escalation the moment SIEM or HRM detected anomalies and risk events show up, so nothing sits unnoticed in someone’s inbox.
Approval & Review Workflow Engine
Structured review processes support multi level approvals, stakeholder comments, and timestamped sign offs, and the whole engine is tied into monitoring systems so accountability and traceability hold up across every compliance operation.
Two data streams, one compliance picture.
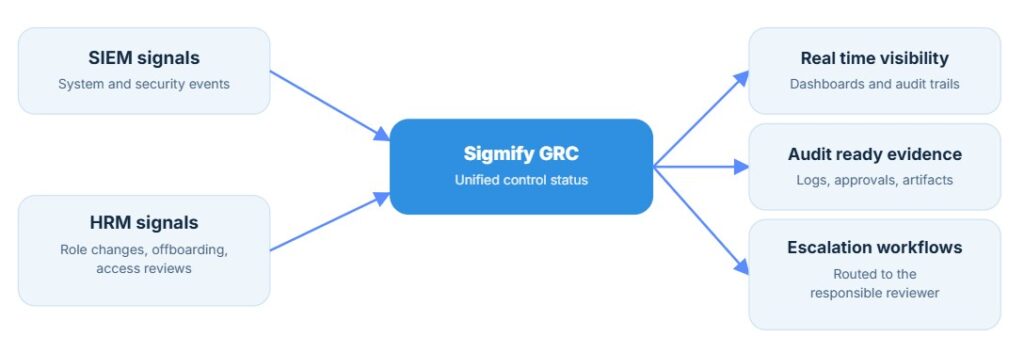
Security events and people events land on the same control record, so nothing gets flagged, escalated, or signed off based on only half the story.
Comprehensive. Timely. Assured.
Comprehensive
The unified control library stays current on its own, mapped across standards such as ISO, SOC, Central Bank, and NIST, with SIEM and HRM integrated monitoring keeping policies, controls, and risks in one place.
Timely
Workflow automation handles access reviews, patch validations, and policy updates, and SIEM and HRM alerts queue the work for the right person, so deadlines get met without anyone chasing them down.
Assured
Real time dashboards and audit trails bring compliance tracking together with SIEM and HRM generated insights, giving leadership honest, evidence-backed assurance instead of a status update taken on faith.
Most GRC monitoring only watches half the risk surface.
SIEM only compliance monitoring correlates security system data against controls, and that's exactly where most platforms stop, leaving everything workforce related out of the picture entirely.
| Term | What it means | Normal GRC action | What Sigmify GRC does |
|---|---|---|---|
| SIEM-only compliance monitoring | Correlating only security system (SIEM) data against controls. | Most compliance monitoring tools stop at system and security events. | Additionally pulls in HRM signals, such as role changes, offboarding, and access review completions, so decisions account for workforce events, not just system events. |
How the pieces actually fit together
Where governance and compliance finally meet
IT governance and compliance management software brings policies, controls, and compliance requirements into one system, and maps them to the frameworks you already answer to, such as ISO, SOC, Central Bank, and NIST. Review, evidence collection, and audit ready workflows all run automatically, so IT operations stay aligned with regulatory and business requirements without someone stitching it together by hand. It’s the difference between chasing compliance after the fact and running it as a continuous, built-in state.
A single source of truth, kept current on purpose
The unified control library is a single source of truth for IT controls, policies, and compliance requirements, mapped across supported frameworks like ISO, SOC, Central Bank, and NIST. SIEM and HRM integrated data keeps it validated and surfaces gaps as they appear, so the library reflects what’s actually happening in the environment, not just what was true at the last manual review.
Built to speak the language of the frameworks you already answer to
The platform maps controls and policies within its IT governance framework to frameworks including ISO, SOC, Central Bank, and NIST.
Two data streams, one compliance picture
By integrating with SIEM and HRM systems, the platform correlates security events and workforce data with control status in real time, so compliance visibility stays current, tasks trigger automatically, and deviations or exceptions surface faster. Neither stream tells the full story alone. Together, they close the gap between what security tools see and what’s actually happening across the workforce.
The blind spot most platforms leave open
Most compliance monitoring tools correlate only security system (SIEM) data against controls. Sigmify GRC also pulls in HRM signals, such as role changes, offboarding, and access review completions, so decisions account for what’s happening with your people, not just what’s happening on the network, closing a gap most platforms leave wide open.
Nothing falls through the cracks
When a task goes overdue, a control fails, or SIEM and HRM detect an anomaly worth flagging, the platform triggers an escalation on its own and routes it straight to the responsible reviewer, with notifications and real time tracking, so an exception never just sits unnoticed in a queue.
Audit day, without the scramble
See your controls, policies, and reviews in one place.
We'll walk through how Sigmify GRC maps to your existing frameworks and where SIEM + HRM integrated monitoring closes the gaps you're dealing with today.