Assessments
Sigmify GRC's Assessments module runs structured, periodic evaluations across governance, risk, compliance, and vendor domains, all from one place. Every assessment cycle, score, and review is backed by real-time SIEM and HRM-driven risk visibility.
Frameworks assessments map to: ISO 27001, SOC 2, NIST, HIPAA, PDPA, DPDPA, GDPR, CCPA, RBI, SEBI CSCRF, and IRDAI. Real-time SIEM and HRM-driven risk visibility is built into every assessment cycle, score, and review.
What Is GRC Assessment Software?
A platform used to plan, distribute, score, and track structured evaluations of governance, risk, and compliance posture.
Vendor Risk vs. Self-Assessment
Vendor risk assessment evaluates a third party. Self-assessment evaluates your own organization.
Do Results Feed Audit Readiness?
Yes. Every response, approval, and score change is captured in the audit trail
Assessment Types, Ownership & Maturity Scoring
Internal maturity assessments, compliance readiness checks, and vendor risk reviews all run on the same scheduling, scoring, and evidence repository infrastructure. What sets them apart is scope and ownership, not separate tools:
- Internal GRC maturity looks at your own control maturity across governance, risk, and compliance.
- Compliance readiness looks at your own controls and readiness against a specific framework or policy.
- Vendor and third-party risk looks at a third-party’s controls and risk posture before or during a vendor relationship.
Maturity itself is scored on a configurable model mapped against SIEM and HRM-sourced risk signals, not a raw compliance percentage, and it rolls into a benchmarking dashboard for cross-department, cross-vendor, and cross-time comparison.
| Assessment Type | What It Evaluates | Typical Owner |
|---|---|---|
| Internal GRC maturity | Your own control maturity across governance, risk, and compliance | Control and process owners |
| Compliance readiness | Your own controls and readiness against a specific framework or policy | Control and process owners |
| Vendor / third-party risk | A third-party's controls and risk posture before or during a vendor relationship | Procurement or vendor-management teams |
A GRC or compliance lead reviews and approves across all three assessment types.
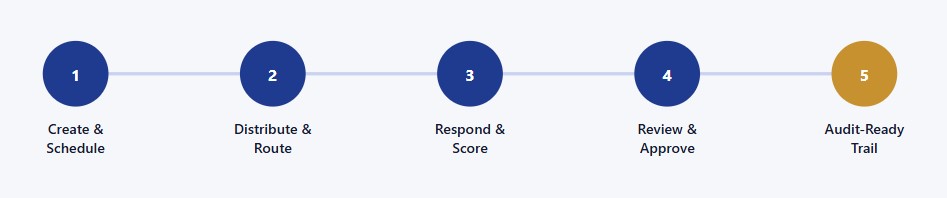
How an Assessment Cycle Flows
| Maturity Level | What It Reflects |
|---|---|
| Initial | Ad hoc or undocumented controls; inconsistent responses |
| Developing | Core controls documented; scoring inputs still largely manual |
| Defined | Structured, repeatable cycles with role-based ownership and evidence capture |
| Managed | Real-time risk signals incorporated; tracked on the benchmarking dashboard |
| Optimized | Maturity trends drive proactive control changes; cross-org benchmarking built in |
Comprehensive. Timely. Assured.
A self-assessment isn’t worth much if it’s only answering last quarter’s risk picture. Sigmify GRC ties every maturity cycle, vendor review, and readiness check to real-time SIEM and HRM-driven insights, so the program moves with the actual risk signal, not just the calendar.
- Escalations trigger automatically when a risk indicator shifts.
- Reviewer workloads rebalance to match where the risk actually is.
3
Assessment types in one module: maturity, readiness, vendor risk
11
Compliance frameworks assessments map to
5
GRC maturity levels, Initial through Optimized
How Sigmify GRC Runs an Assessment, End to End
From cycle creation through audit-ready history.
Creation, Scheduling & Ownership
Cycles Assigned to the Right Person, On Schedule or On Demand
Structured questionnaire workflows are created and distributed for IT risk, compliance frameworks, and process evaluations, integrated with SIEM and HRM insights to stay aligned with real-time risk indicators.
- Cycles launch on a fixed schedule or on demand.
- Questions route to the right stakeholders, with centralized tracking.
- Maturity cycles typically run quarterly or semi-annually.
- Individual questionnaires trigger ad hoc for a new vendor, a risk event, or a framework update.
Scoring & Benchmarking
Maturity Scoring That Reads Risk Data, Compared Across the Org
- Maturity scores land on a
benchmarking dashboard. - Comparisons run across departments, functions, or vendors.
- Trends are tracked over time, not as a one-off snapshot.
Evidence, Approval & Audit Trail
Nothing Gets Lost Between a Response and an Audit
Responses, attachments, and reviewer inputs are stored in a centralized evidence repository with complete traceability.
Every response routes through defined review and approval stages.
- Real-time status updates and notifications keep reviewers on track.
- Every response, approval, and score change lands in a complete, time-stamped audit trail, aligned to SIEM and HRM event logs.
- Results are ready for audit and compliance reporting without separate reconciliation.
Stay ahead of the IRDAI 2026 guidelines
Know how Sigmify GRC's IRDAI compliance software helps you stay compliant — including the 6-hour incident reporting deadline and DPDP alignment requirements.