Global Security & Compliance Standards Supported by Sigmify GRC
Data security and privacy standards define the frameworks organizations rely on to protect sensitive and regulated information, including ISO 27001, SOC 2, GDPR, HIPAA, NIST, and DPDPA. Sigmify GRC combines control mapping software, AI-driven insights, and native integration with enterprise systems, SIEM platforms, and security tools into one framework-agnostic GRC platform.
Multi-Framework Management, in One Platform
Run every standard you answer to in parallel from one platform, instead of implementing them one after another as separate projects.
Updates That Follow Every Mapping
When you change a shared control, the update carries through automatically to every framework it’s mapped to, so no standard is left running on an old version.
One Control Set, Every Audit
One mapped control satisfies overlapping requirements across every standard it applies to, and its evidence is captured once instead of being gathered separately for each audit.
Adding a Framework Doesn’t Mean Starting Over
A new standard extends your existing control set through cross-framework mapping, instead of needing a separate implementation.
At a glance
Compliance Framework Comparison
ISO 27001 and SOC 2 are voluntary but often required by contracts or customers. GDPR, HIPAA, and DPDPA are mandatory wherever they apply. NIST is voluntary overall, but mandatory for US federal contractors under 800-53. The table below places all six side by side for direct comparison.
| Framework | Type | Status | Best For | Typical Timeline |
|---|---|---|---|---|
| ISO 27001 + 27002 · 27005 · 27017 · 27701 · 22301 | Certification | Voluntary | Organizations needing a globally recognized ISMS certification | 3–6 months |
| SOC 2 | Attestation | Voluntary | SaaS and service organizations selling to US enterprise customers |
2–4 mo (Type I) 6–12 mo (Type II) |
| GDPR | Law / Regulation | Mandatory | Any organization handling EU resident data | Ongoing — no fixed cycle |
| NIST CSF / 800-53 | Framework | Voluntary | US enterprises and government contractors building a risk program | Ongoing — phased maturity |
| HIPAA | Law / Regulation | Mandatory | Healthcare organizations and their vendors handling PHI | Ongoing — no fixed cycle |
| DPDPA | Law / Regulation | Mandatory | Any organization handling personal data of individuals in India | Ongoing — phased rollout |
Timelines are directional and vary by organization size, existing controls, and audit firm — validate against your specific scope before planning.
Where the overlap lives
The Same Controls, Reused Across Six Audits
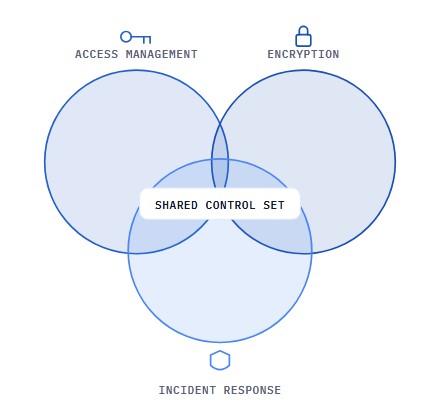
Every framework above asks a version of the same three questions: who has access, whether data is protected, and what happens if something goes wrong. Sigmify GRC maps one control set to answer all three.
The Sigmify GRC Approach
Always Ready, Never Reassembled
- Auditors and assessors draw from one continuously current control set.
- There are no framework-specific spreadsheets to maintain separately.
Every Standard, One Screen
- A single dashboard shows control health across every standard you run.
- There’s no need to switch between framework-specific views.
Standard by Standard
ISO 27001
The Full ISO/IEC Stack, Under One Roof
- Implement and manage ISO 27001, 27002, 27005, 27017, 27701, and 22301 together.
- Automated control monitoring supports centralized governance.
- Cross-framework mapping integrates with SIEM, HRM, and cloud platforms.
SOC 2
Faster Attestation, Built on Automation
- Automated control mapping, evidence collection, and real-time monitoring align with the Trust Services Criteria.
- IAM and cloud connections, combined with SIEM integration,
enable continuous monitoring. - The result is faster audits and improved customer trust.
GDPR
Personal Data, Tracked From Consent to Breach Notice
- Automated data discovery, consent management, and DSAR workflows support GDPR compliance.
- Integrations with DLP, IAM, and security monitoring tools help protect personal data.
- This is part of global privacy compliance software that also covers India’s DPDPA.
NIST
Risk Management, Continuously Monitored
- Sigmify GRC aligns with NIST CSF and NIST 800-53 within one unified compliance framework.
- Integrations with SIEM, vulnerability scanners, and threat intelligence platforms enable continuous monitoring.
- This supports proactive, software-driven remediation.
HIPAA
PHI, Handled With Its Own Safeguards
- Access controls, encryption, and audit-readiness logging protect PHI.
- Connections with IAM, DLP, and endpoint security (EDR/XDR) safeguard healthcare data.
- A dedicated HIPAA guide covers the full Security Rule breakdown separately.
DPDPA
India's DPDPA, Aligned With the Standards Already in Place
- Consent management, data lifecycle governance, and breach-readiness workflows support the Act’s phased rollout.
- This approach also aligns with ISO 27001, SOC 2, and GDPR.
- Organizations operating across both the EU and India can manage overlapping obligations from one system.
Value Delivered
Continuous Monitoring, Not Point-in-Time Audits
- Risk, controls and audit readiness are monitored continuously.
- You see changes as they happen, not at the next audit.
Connected to the Tools You Already Run
- Sigmify GRC connects with SIEM, IAM, DLP, HRM, EDR/XDR, vulnerability scanners, threat intelligence platforms and cloud systems.
Not sure where to start? Our team can map your existing controls against any combination of the standards above.