Simplify Governance, Risk & Compliance End to End
Governance, risk, and security, run from one platform instead of five different tools. That's the short version of what Sigmify GRC does. The rest of this page is the long version.
What to Look For in a GRC Platform
Most GRC platforms look similar on a sales call. The differences show up later, usually during an audit. Four things are worth checking before you sign anything:
| What to Check | What It Actually Means |
|---|---|
| Checklist Depth | A compliance checklist library deep enough to cover every framework you're actually audited against, not just the popular ones. |
| Owned Task Automation | Workflow automation that assigns and tracks every task to a named owner, not just a shared inbox. |
| Early-Warning Monitoring | A monitoring view that surfaces defaults before an auditor does. |
| Connected Data | Integration points such as SIEM, HRM, and your existing vendor stack, so compliance data doesn't live in a separate silo from the rest of the business. |
The six capabilities below are how Sigmify GRC answers each of those, one row at a time.
Addressing the Information Security Challenge
Security compliance usually breaks down in the handoff between teams. Sigmify GRC closes that gap with one approach run in three steps: Scan & Setup, Perform, and Monitor, tying governance and risk workflows to SIEM- and HRM-driven security signals.
Step 1 — Scan & Setup
- Scans your environment
- Sets up the compliance frameworks you need, on your own timeline
- Loads a ready-to-use checklist library with best-practice suggestions built in
Step 2 — Perform
- Assigns every task to a named owner through built-in workflow automation
- Sends automated alerts before tasks fall due
- Routes missed tasks into a dedicated exception workflow
Step 3 — Monitor
- Puts a live compliance dashboard in front of you
- Flags defaults early, with SIEM and HRM signals feeding in at this stage
- Keeps you looped in on business continuity
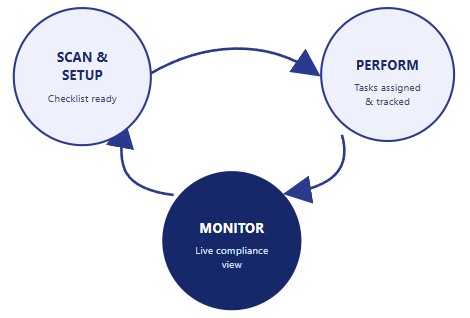
The cycle repeats — Monitor's findings feed the next Scan & Setup, so the framework keeps up as your environment changes.
How Sigmify GRC Helps, Step by Step
Sigmify’s IT governance, risk, and compliance solution combines solid security practices with auditing that doesn’t slow your team down. Here’s what’s actually behind each stage.
Setup
Nothing Built From Zero
- A ready checklist library covers every standard you support
- Adopt frameworks on your own timeline, with best practice suggestions built in
- One structured, multi framework checklist keeps everything consistent
Effective Operations
Every Task Has a Name Attached
- Clear ownership and full workflow visibility, so tasks don’t get lost
- Automated alerts before things become due, not after
- A dedicated workflow for exceptions when things don’t go to plan. See our Compliance & IT Governance page for the full model
Monitoring
Problems Surface Before They Spread
- A live dashboard tracks progress across every framework you run
- Defaults get flagged early, before they become a bigger issue
GRC Platform Features at a Glance
Six capabilities sit behind those three steps.
| Capability | What It Does |
|---|---|
| Framework & Checklist Library | Pre-built checklists for supported regulatory frameworks, covering multi framework compliance checklist needs out of the box. See our Standards page for the full list. |
| Compliance Workflow Automation | Task assignment, due-date alerts, and approval routing across your compliance calendar. |
| Compliance Monitoring Dashboard | A single dashboard view of task status, defaults, and audit readiness. |
| SIEM & HRM Integration | Security-event and human-risk signals feed directly into your compliance posture. See our dedicated SIEM & HRM Continuous Compliance Monitoring page for how the integration works. |
| Exception & Escalation Management | Structured handling of missed tasks and risk exceptions. See our Compliance & IT Governance page for detail. |
| Vendor & Third-Party Risk Management | Extends the same checklist-and-workflow model to your vendors. See our Vendor Risk Management page for detail. |
Trusted Across Compliance Teams
Frameworks supported, tasks automated, and defaults caught before they become incidents. These are the numbers buyers check first.
Built Around How Teams Actually Use It
Flexibility
Adopt as Is, or Make It Yours
Run the frameworks exactly as delivered,
or adapt them to policies you already have.
BEACON AI
AI That Does the Watching for You
Beacon AI finds personal data across your systems, ranks tasks by risk instead of arrival time, and maps new regulatory circulars to the policies they affect. People still make every compliance decision; Beacon just makes sure they see what matters first.
AUDIT READY
The Evidence Is Collected Before Anyone Asks
Documents, screenshots, and system logs are captured and time stamped as work happens, then reused across frameworks wherever controls overlap. When audit time comes, the report builds itself from linked workpapers: scope, findings, and corrective actions included.