GRC as a Service: End to End Compliance, From Assessment to Execution
We assess your compliance posture, help you implement what's missing, and keep watching it over time, combining expert led reviews with real time signals from your SIEM and HRM systems.
Who it’s for
Teams without a dedicated compliance function, organisations facing their first certification audit, and businesses juggling several frameworks at once with the same small team.
What it covers
ISO 27001, SOC 2, DPDPA, RBI and SEBI cybersecurity requirements, and other frameworks your regulators or customers hold you to, all run under one engagement.
What you get
A clear assessment of where you stand, a prioritised remediation plan, audit ready evidence, and regular posture reports, so you always know what’s done and what’s next.
The Approach
How It Works
One continuous engagement made up of three stages that build on each other.
01
Assess
We start with a structured self assessment, then our specialists review it to confirm where you actually stand on risks, controls, and compliance effectiveness.
02
Implement
Our team works directly with your stakeholders to build secure infrastructure and put data protection controls in place.
03
Monitor
Compliance monitoring and governance workflows then run continuously, so your posture stays current.
Why It Matters
Compliance That Keeps Pace With You
Regulations don't sit still, so the way you track your compliance shouldn't either.
Built around you
Sigmify’s own compliance and security specialists work alongside your team from the first assessment onward, so there’s always someone to call.
Real signals, not just self reported answers
SIEM and HRM data feed into the same picture, so what you report reflects your actual technical and human attack surface.
One model, every regulation
The same three stage approach carries across whichever framework applies to you, so your team learns one process, once.
Scope of Work
What's Included
Every GRCaaS engagement covers five managed services, bundled together rather than sold piece by piece.
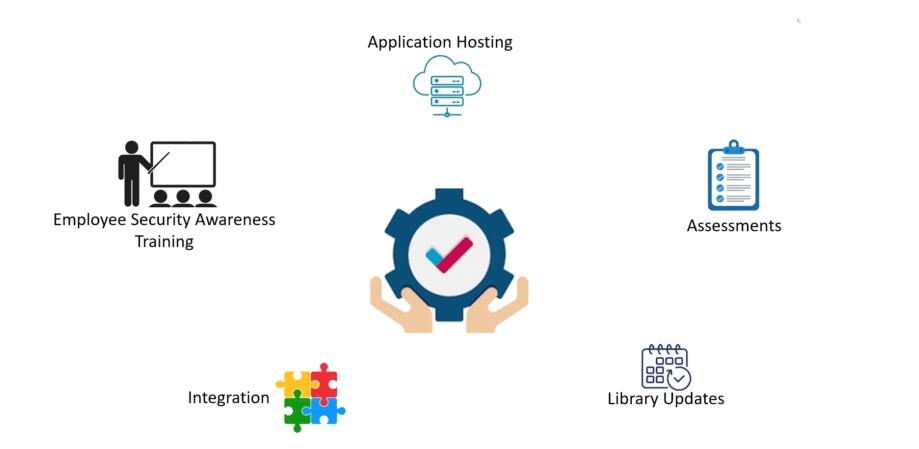
Application Hosting. We host the platform components your engagement relies on, so your team doesn’t have to run anything itself.
Assessments. Structured assessments repeated throughout the engagement, each one reviewed by our specialists.
Integration. We connect your existing SIEM and HRM tools into the compliance picture, so your security and HR data actually feed the program.
Library Updates. Your framework and control library stays current as regulations evolve, without you having to track every change yourself.
Assessments. Structured self assessment paired with expert led review, delivered on an ongoing basis rather than as a one time exercise.
The Difference
GRC as a Service or Self Serve?
vs. Self Serve Modules
Same Platform, More Support
Sigmify’s Assessments and Compliance and IT Governance modules are self serve tools you can run yourself. GRC as a Service uses that same platform, with our specialists driving it for you.
See How GRC as a Service Handles Compliance End to End
Tell us where your compliance program stands today, and we'll walk you through what a GRC as a Service engagement would look like for your team.